Network engineering
Enterprise Network Security: Segment Services and Control Administrative Access
Design practical network security controls around service dependencies, enforced boundaries, privileged access and tested recovery.
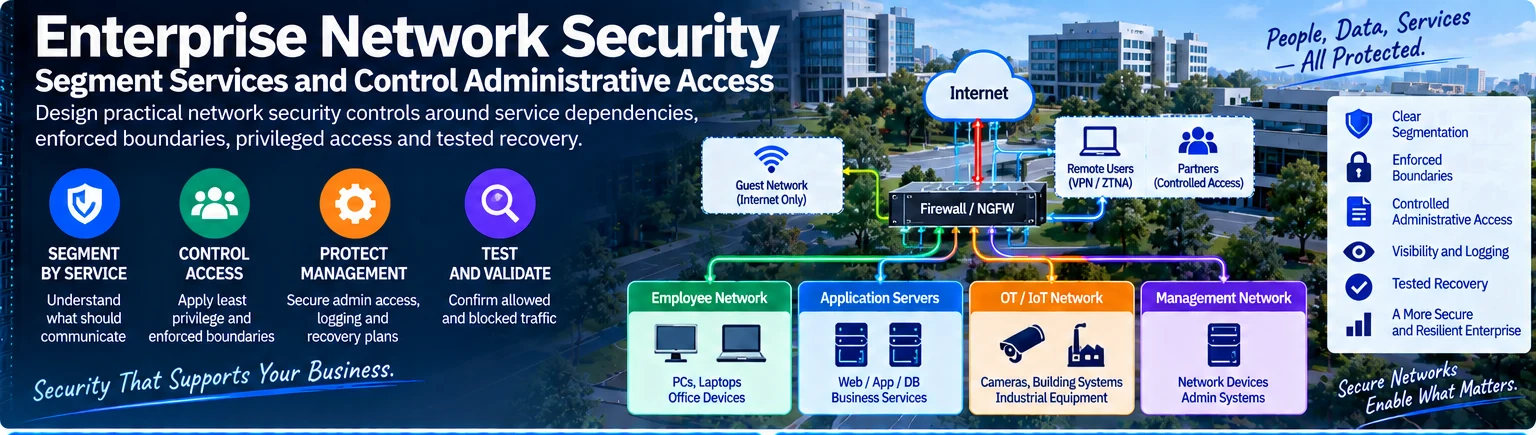
A network security design should explain which communications are allowed, where those decisions are enforced and how exceptions are managed. Adding a firewall or creating more VLANs does not establish that the intended boundary exists. Start with service dependencies and operating ownership.
Build an allowed-communications matrix
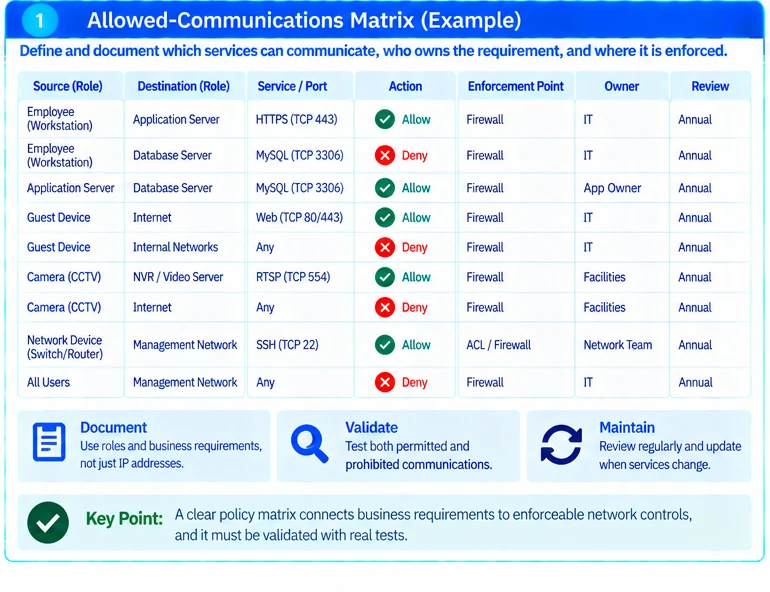
Group endpoints by function and risk-relevant requirements: employee access, guest devices, servers, cameras, infrastructure management and specialized systems. Identify the business owner of each required communication path.
An illustrative matrix might permit employee devices to reach an application service, allow that service to reach its database, and deny direct employee-to-database access. This is a design example, not a universal policy; the actual application dependencies must be confirmed before enforcement.
| Policy record | Required information |
|---|---|
| Source and destination roles | The systems involved, not only current IP addresses |
| Service | Protocol, port and application purpose |
| Enforcement point | Device or service responsible for the decision |
| Owner | Person accountable for the business requirement |
| Review condition | Expiry, change trigger or recurring review |
| Validation | Positive and negative tests demonstrating the boundary |
Separate network location from authorization
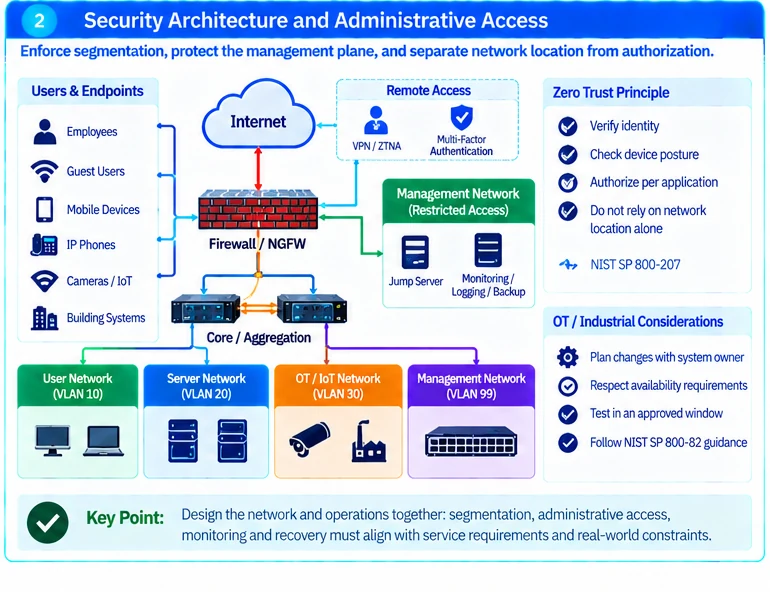
A device being on an internal subnet should not automatically grant access to every internal service. NIST’s zero-trust architecture frames access decisions around resources and authorization rather than an implicit trust in network location. This is an architectural principle, not a claim that a particular switch or firewall creates a complete zero-trust deployment. R35
Apply identity, device and application controls where the environment supports them. Keep the responsibilities of network segmentation and application authorization distinct.
Protect the management plane
Restrict administrative interfaces to an approved access path. Define privileged accounts, logging, configuration backups and recovery procedures. Avoid exposing management services merely because remote support is convenient.
A separate management network is useful only when its access policy and dependencies are understood. Test whether recovery access survives the production-network failure it is intended to address.
Respect operational constraints
For industrial or other operational technology, coordinate changes with the system owner and safety process. Availability and deterministic behavior may constrain testing and maintenance. NIST’s OT security guidance addresses these distinct operational requirements; it should not be replaced by an ordinary office-network checklist. R34
Validate both permitted and prohibited paths
Confirm that required applications still work, then test that unauthorized cross-boundary communications are blocked as intended. Record rule owners and approved exceptions. Deploy changes in a scope that permits diagnosis and rollback rather than introducing many untested policy changes at once.
The result is a traceable control design with evidence, not a blanket promise of security or regulatory compliance. Product selection follows from the required enforcement, visibility and capacity; it should not substitute for defining those requirements.
Engineering illustrations
These figures illustrate the design concepts discussed here. They are not measured results, certified configurations or a supplied-equipment list.